
Security and Compliance
Security you can trust from day one
When we assemble your program on M4 (formerly Mobiconnect), Mobiddiction’s platform, we protect your data, your users' privacy and your reputation, under a certified Information Security Management System.
ISO/IEC 27001:2022
Certified by an independent, accredited auditor
Developed and operated under Mobiddiction’s Information Security Management System, certified to ISO/IEC 27001:2022 by an independent, accredited auditor.
The certificate’s scope covers “the design, development, hosting and support of Mobiconnect powered digital applications and platforms operated by Mobiddiction”. M4 sits within that certified scope.
Certification demonstrates that we identify and manage information security risks, maintain robust access, encryption and incident response controls, and undergo continual improvement through annual audits and management review. For NSW Government and Enterprise clients, it provides verifiable assurance that our systems meet mandated security and privacy obligations.
Secure by Design
We start by asking what data we can avoid collecting
Since Mobiddiction was founded in 2012, we have delivered projects in health, finance, public safety and other regulated environments where trust is critical. Our teams include senior leaders and principal engineers with more than twenty years of experience in secure IT delivery, including over a decade inside high security government programs. That experience shaped our secure by design philosophy well before we began formal certification.
Secure by design means every project starts with one question: can the outcome be achieved without collecting personal or sensitive data? If not, what is the minimum data required, and how do we reduce exposure at every stage of the system life cycle? We treat data minimisation as a first principle, because an organisation cannot have a breach of information it never collects.
When sensitive or regulated data must be processed, we evaluate the risks, controls and obligations with the client and choose the least complex, safest way to achieve the goal.
Safeguards designed to keep vulnerabilities out
From first commit to deployment, M4 is designed to keep vulnerabilities out.
Pre-deployment scanning
Code is automatically checked for common security issues before every deployment.
Secrets management
API keys and credentials are encrypted and stored securely, with guards against accidental exposure.
Least privilege by default
Role-based access control, multi-factor authentication, single sign-on with Google (with Microsoft and GitHub supported) and workspace-level permissions ensure people and systems only see what they need.
Infrastructure protection
Programs run on AWS infrastructure in Sydney, with strong physical and network security. Where compliance requires it, a program can run on its own separately provisioned infrastructure, on the same M4 codebase, released on its own schedule.
What M4 does for every program
Hosted in Australia
Programs run on AWS in Sydney, behind a content delivery network.
Multi-factor sign-in
Authenticator-app multi-factor authentication for staff and app users.
Rate limiting and security headers
Per-key and per-IP rate limiting, and security headers on every response.
Privacy tools for app users
Self-service account deletion and a personal-data export.
Bot protection on public forms
Cloudflare Turnstile or reCAPTCHA on public submissions.
The Journey to Certification
Evidence procurement teams can review
Our ISO/IEC 27001 program formalised the controls, standards and operational processes we had already established over many years. Certification confirms that our Information Security Management System meets international best practice in risk management, policy governance, operational security, supplier management and continuous improvement.
The journey included documenting business-wide risk treatment plans, hardening our internal cloud infrastructure, defining asset management and incident response models, establishing staff training pathways and mapping our secure development practices to the Annex A controls. It also strengthened change management, audit logging, access governance and monitoring across M4, which runs NSW Government programs such as SharkSmart.
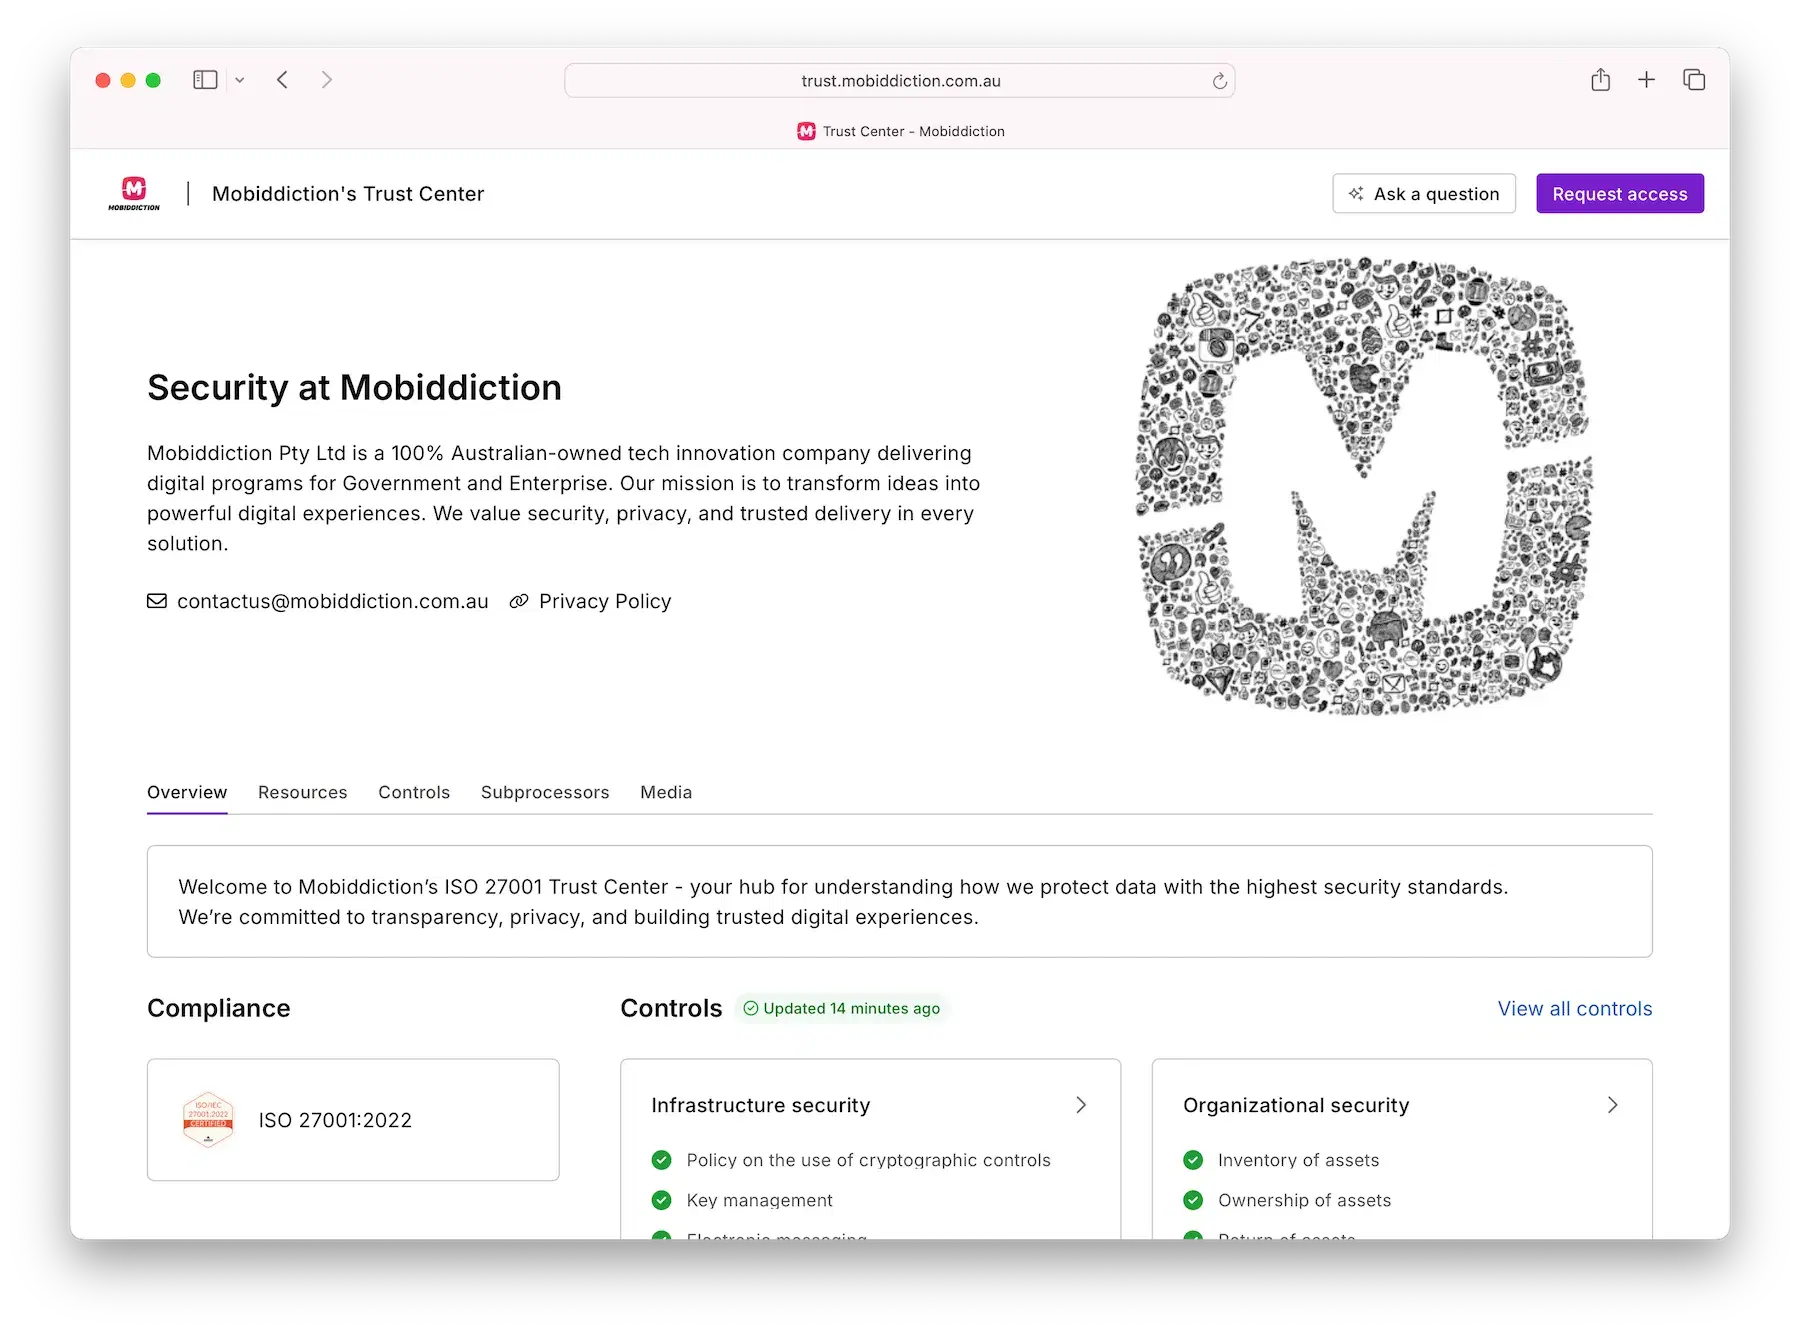
Our certification is backed by ongoing internal reviews, annual surveillance audits and regular external audits. Our Trust Centre at trust.mobiddiction.com.au is where procurement teams can access our controls, policies and governance documentation, and review the evidence behind our compliance program.
Controls embedded in every delivery team
We apply structured risk management across the full life cycle of a system, and design cloud and application architectures in line with AWS best practice. Our ISO/IEC 27001 controls are embedded in every delivery team, from engineering and DevOps to geospatial, product and support, so the whole organisation works to one security posture.
Secure coding and peer review
Secure coding practices with mandatory peer review on every change.
Static and dynamic analysis
Static and dynamic code analysis run as part of the development pipeline.
Segregated environments
Development, staging and production environments are kept separate.
Access control and 2FA
Role-based access controls and two-factor authentication for all operational systems.
Vulnerability scanning
Continuous vulnerability scanning and dependency management.
Incident response
Structured incident response and reporting.
Runbooks and training
Documented operational runbooks and staff training.
Full traceability
Full traceability of deployments and configuration changes.
Complex Compliance Requirements
A decade of work in regulated sectors
Mobiddiction has more than a decade of experience in the health sector, where privacy and secure data handling are paramount. Our work includes PatientVR and VapingVR for NSW Health, early stage Apple Watch health projects in collaboration with Mayo Clinic, and health and wellness programs with partners such as SP Health. We also support confidential patient, nurse and medical education programs with pharmaceutical and health organisations, and children’s wellbeing initiatives with the Starlight Foundation, giving us a mature understanding of Federal and State health privacy requirements in NSW and Queensland.
Our financial sector work added compliance exposure around identity, secure onboarding, transaction visibility, staff confidentiality and auditability. It strengthened our ability to design systems that satisfy high assurance identity controls, formal risk registers and strict operational segregation standards.
Our systems are designed with privacy in mind, encompassing the Australian Privacy Act and the Australian Privacy Principles, and our privacy tools are made for the obligations our clients operate under, including self-service deletion and data export for people who use their apps.
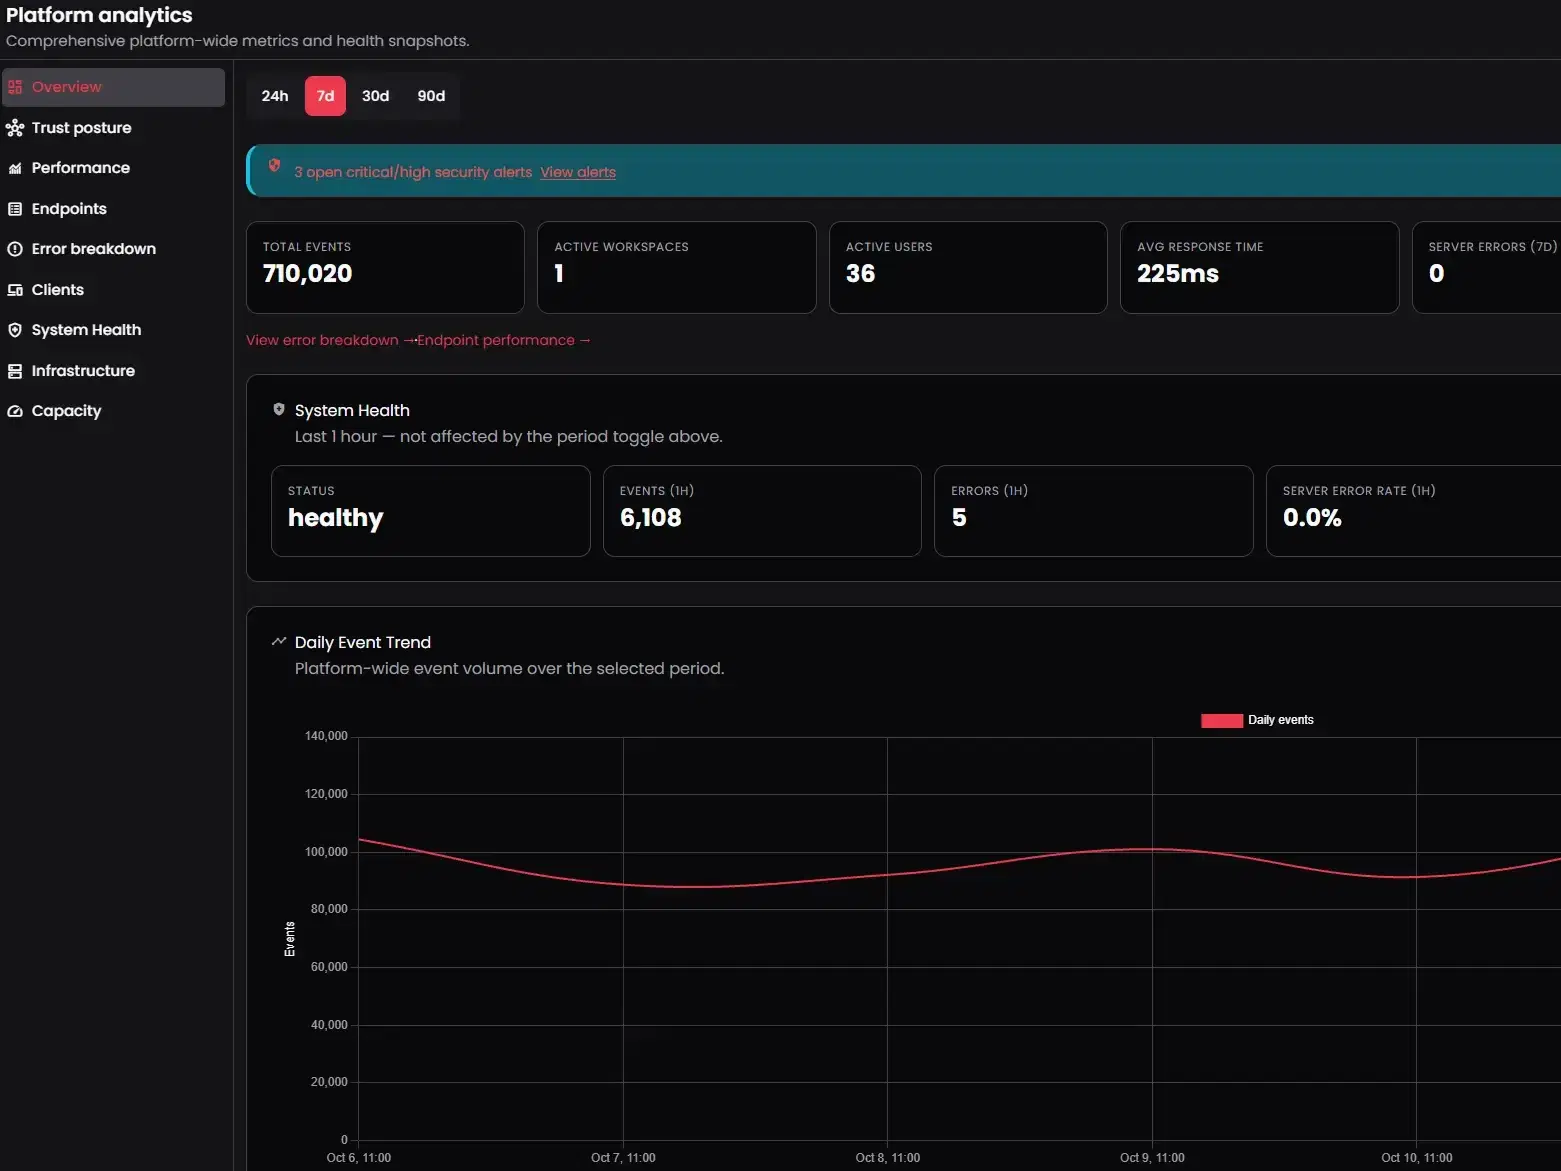
Threats evolve every day. So do we.
We run continuous security reviews and monitoring alongside third-party tools. M4 applies per-key and per-IP rate limiting and security headers to every response, and where compliance requires it a program can run on its own separately provisioned infrastructure.
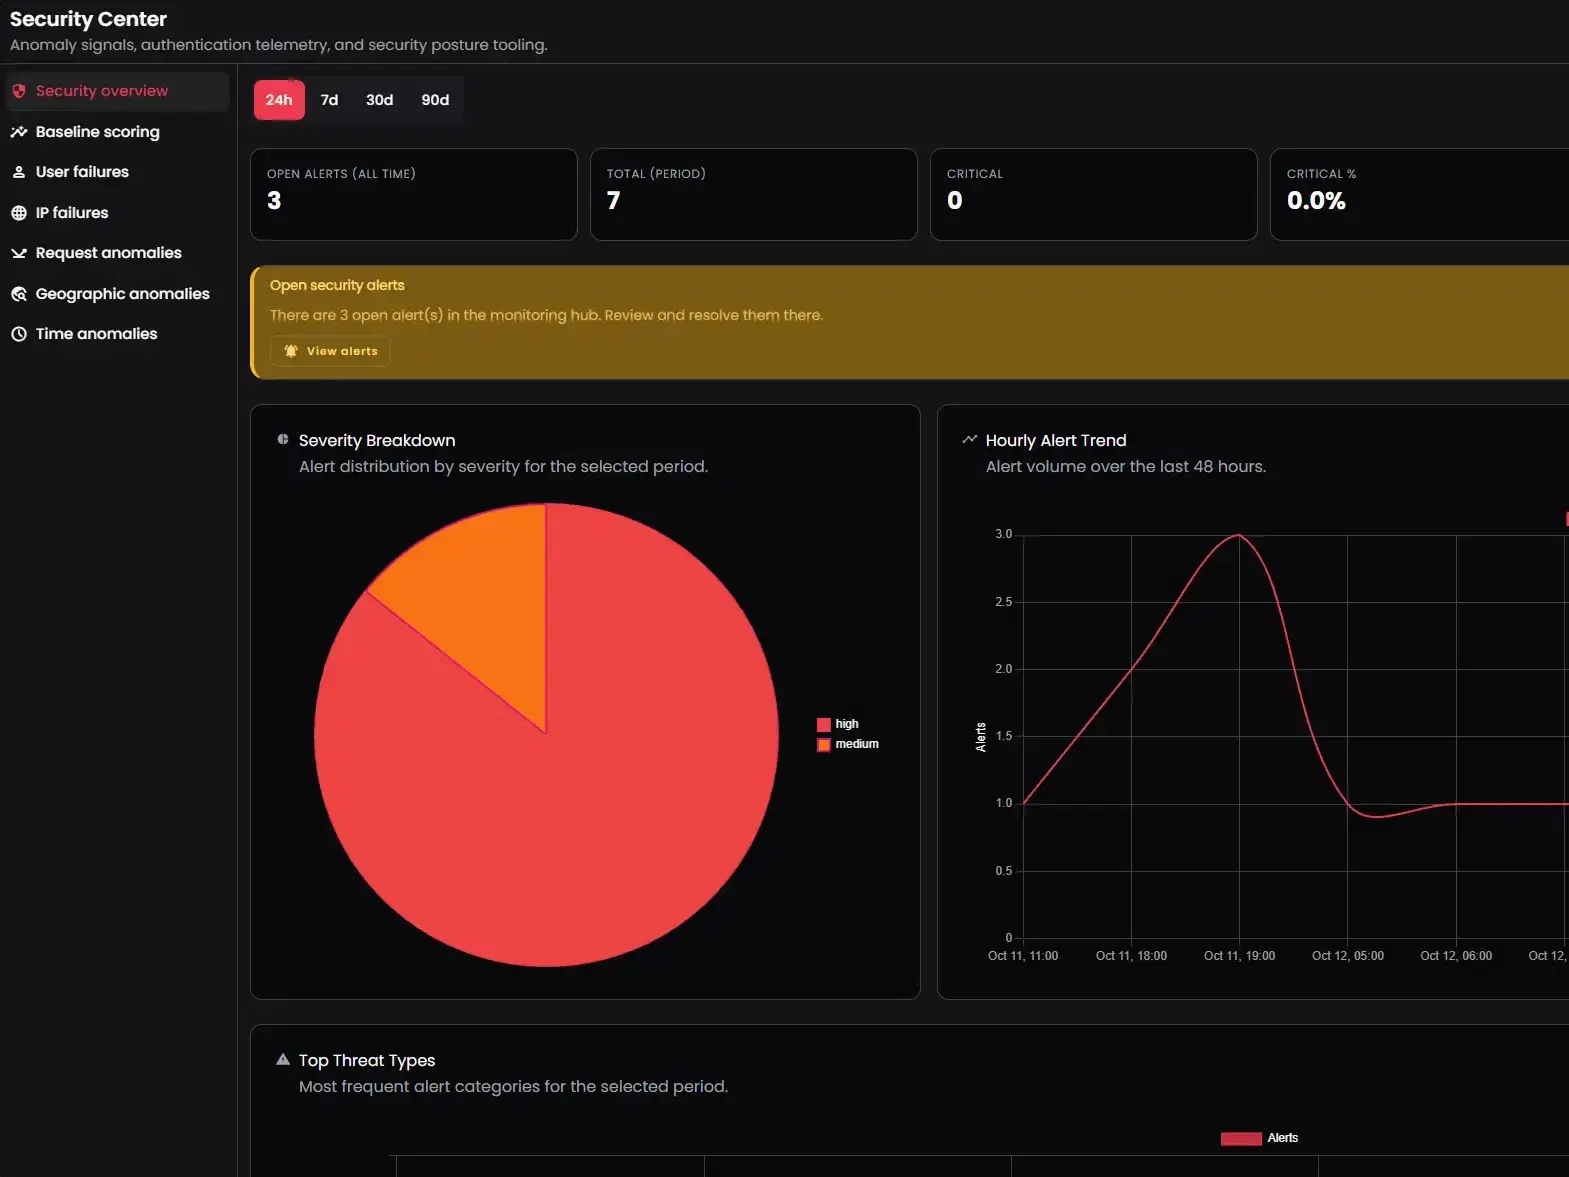
Security is never set and forget
Our security posture, certification and controls are published in our Trust Centre, with policies and audit evidence available to procurement teams there. We welcome responsible disclosures: if you spot something, we’ll act quickly. And we keep investing in new protections, automated scanning and threat research.
Assurance that holds over long timeframes
Procurement teams need assurance that a supplier can deliver securely at scale and maintain that posture over long timeframes. Mobiddiction has done so for more than a decade across state agencies, national organisations and large enterprises, with senior leadership directly involved in governance, architectural oversight and risk management.
Security that reduces risk at every step of your program
Get in touch for a discovery session with our team. We love tech, but speak human.